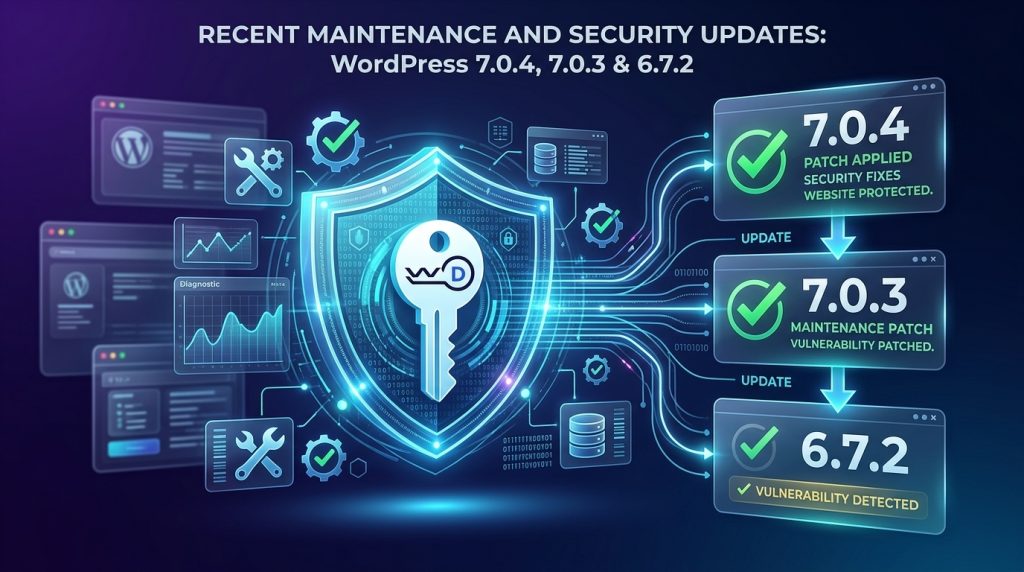
Managing a commercial WordPress platform requires continuous operational vigilance. Over the past several weeks, the WordPress core security team deployed a rapid series of critical patches targeting high-severity vulnerabilities across both modern release tracks and legacy installations.
For digital executives, engineering leads, and e-commerce operators, treating these announcements as routine maintenance is an unacceptable business risk. High-severity exploits don’t wait for business hours—they are targeted by automated global botnets within hours of public disclosure.